
Imagine a WhatsApp message arriving late in the afternoon.
The profile looks like a regular supplier.
The message says the bank account for today’s invoice has changed.
The amount is correct.
The supplier name is correct.
The finance team is rushing to meet a payment cut-off.
There are two possibilities.
The request is genuine.
Or someone needs only a few minutes of misplaced trust to redirect company money.
That illustrates an important feature of modern fraud.
Attackers do not always need to hack the system.
Sometimes they only need to hack the decision process around the system.
The scale is already significant
Indonesia Anti-Scam Centre, or IASC, provides a sense of the scale.
From its launch on November 22, 2024 through July 31, 2026, IASC received 637,055 public reports.[1]
A total of 1,179,881 accounts were reported and verified, while 607,210 accounts were blocked.
Approximately Rp724.1 billion in scam-related funds were blocked, and around Rp204.3 billion had been returned to victims.[1]
These are not business-victim statistics specifically.
But they demonstrate that financial scams are no longer marginal events.
Digital payment activity continues to expand
The answer is not to reverse digitalisation.
By June 2026, QRIS had reached 65.77 million users and 44.86 million merchants, with 96.68% of merchants classified as MSMEs.[2]
QRIS processed 12.55 billion transactions worth around Rp1.12 quadrillion in the first half of 2026.[2]
Greater adoption creates enormous efficiency.
It also makes payment controls more important.
Not because digital payments are inherently unsafe, but because more channels, more administrators and faster settlement can allow both error and manipulation to move faster.
Fraud often targets people, not infrastructure
Security discussions often focus on passwords, firewalls and malware.
Scams frequently take another route.
Satgas PASTI identifies impersonation as a recurring method: criminals misuse the identity or attributes of legitimate institutions to request credentials, verification codes or funds.[1]
Inside a company, the underlying technique can appear as:
supplier impersonation;
executive impersonation;
fake invoices;
fraudulent beneficiary changes;
refund fraud;
or compromised accounts.
The important question becomes:
Can the payment process itself be socially engineered?
The most dangerous request may look completely normal
Badly executed fraud can be obvious.
Poor spelling.
Strange amounts.
Unknown senders.
Effective fraud often looks routine.
The payment value is normal.
The vendor is known.
The invoice looks familiar.
The timing makes sense.
Attackers may know real project or organisational details.
That is why judgement alone is not enough.
High-risk actions need controls that activate even when the request appears legitimate.
Treat beneficiary changes as high-risk events
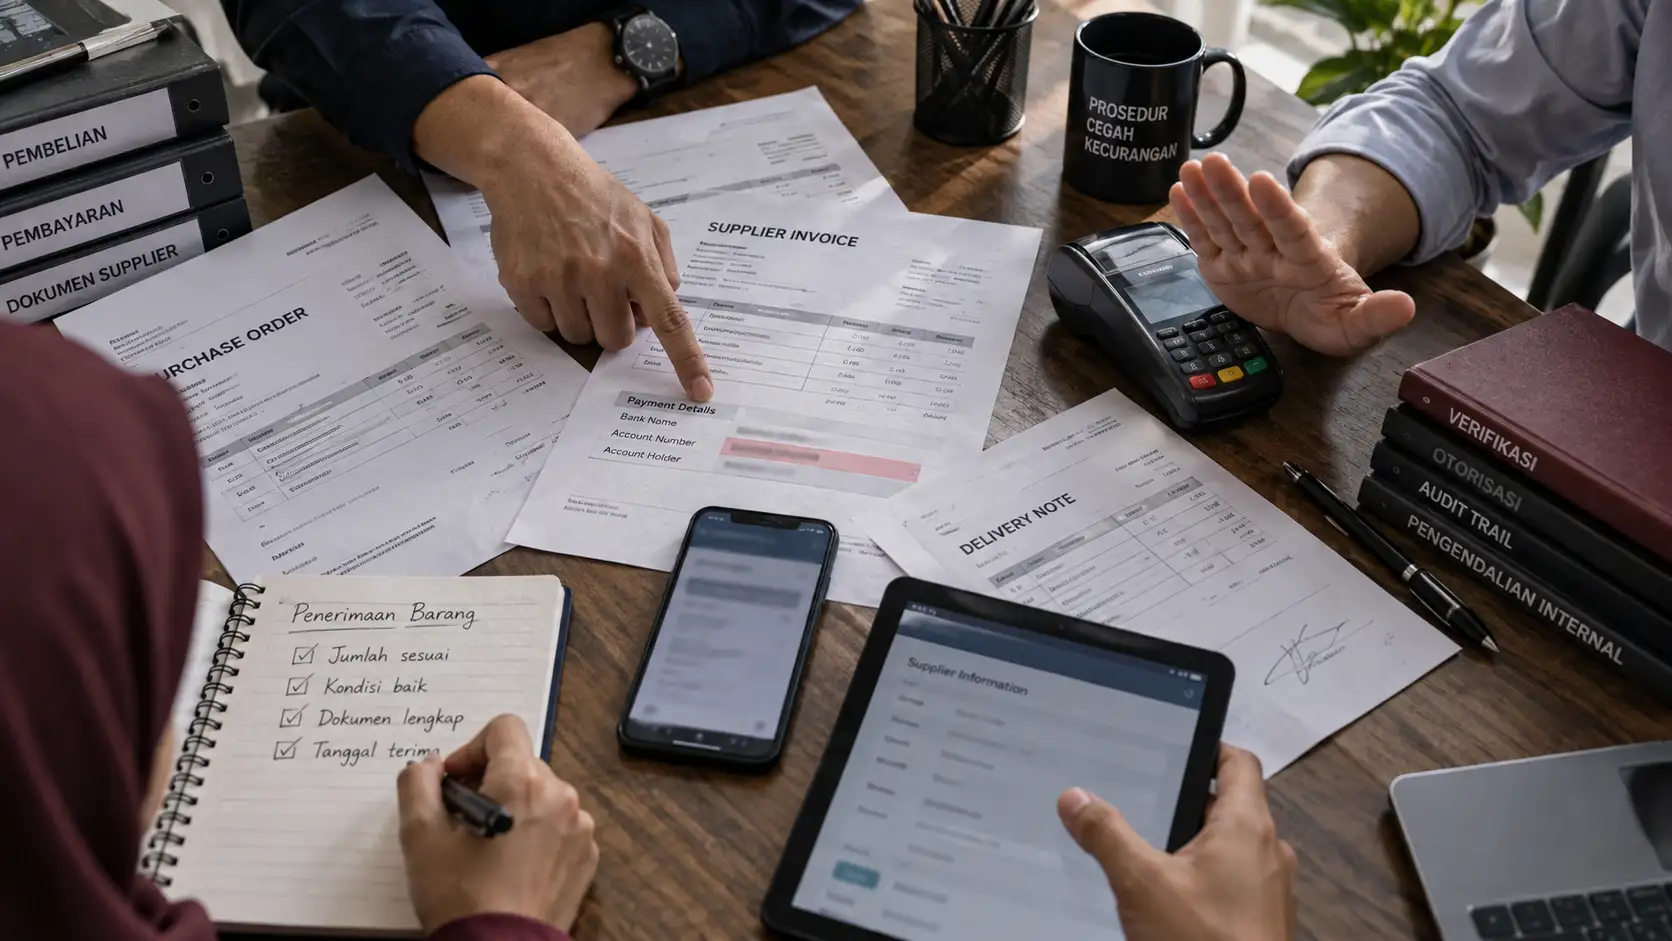
A change in a vendor’s bank account should not be treated as routine administration.
Do not change payment master data purely from an email, message or PDF sent through the same channel requesting the change.
Verify independently.
Use an existing, previously validated contact.
For material changes, require a second approval.
Record evidence of verification.
The core issue is not whether the vendor name is correct.
It is whether the destination of funds has changed.
Use maker–checker controls
The person preparing a payment should not always be the sole person approving it.
Maker–checker creates separation:
one person prepares;
another verifies;
the payment is then executed.
Thresholds can vary.
A small recurring payment does not need the same control as a large transfer to a new beneficiary.
What matters is that high-impact actions do not depend on a single person.
Urgency should not cancel verification
Scammers frequently create urgency.
The payment must happen today.
The director is unavailable.
The supplier will stop delivery.
The instruction is confidential.
Urgency shifts attention from verification toward speed.
Businesses need a simple principle:
urgent requests still follow control requirements.
A genuinely urgent payment should trigger faster verification—not no verification.
A screenshot is not settlement
For retailers and F&B businesses, one of the simplest scams remains relevant:
a customer displays proof of payment.
The cashier accepts the image.
Goods are handed over.
The money never arrived.
Payment should be verified from an internal source:
merchant application;
bank account;
POS integration;
or settlement system.
A screenshot proves the existence of a screenshot.
It does not necessarily prove that funds settled.
Refunds need destination controls
Refund fraud can occur when money is requested back to a different account from the original payer.
Where system capabilities allow, refunds should generally return through the original payment method or validated origin.
Exceptions should receive additional review.
The principle is simple:
changing the destination of money increases risk.
Apply role-based access
Not every employee needs every permission.
Customer-service staff may need order information.
They may not need access to settlement-account settings.
Warehouse staff need delivery records.
They do not need banking permissions.
A finance user may create payment batches without holding final approval rights.
This is the principle of least privilege.
Smaller permissions reduce the damage a compromised account can cause.
Learn from transaction-level fraud detection
Bank Indonesia has strengthened fraud-management requirements in BI-FAST.
Participants are required to maintain fraud-management systems, including account- and transaction-level fraud detection as a first line of defence.[3]
Ordinary businesses do not need bank-scale technology.
But they can apply the same concept.
Flag transactions that are unusually large.
Involve a new beneficiary.
Occur at unusual times.
Break established patterns.
Or combine multiple changes at once.
An anomaly is not automatically fraud.
It deserves review.
Reconciliation is also a security control
Reconciliation is usually considered an accounting process.
It is also fraud detection.
Match:
orders;
invoices;
goods received;
payments;
bank movements;
refunds;
and settlements.
The faster reconciliation occurs, the faster unusual transactions become visible.
Bank Indonesia’s payment-system framework itself recognises reconciliation, transaction security, fraud prevention and risk mitigation as key functions.[4]
Create a “never approve by chat only” list
Businesses can explicitly identify actions that require a second channel.
For example:
vendor bank-account changes;
large payments;
beneficiary changes;
administrator-access changes;
payroll-account changes;
large refunds;
or first payments to a new supplier.
Messaging can start a request.
It should not necessarily complete the authorisation.
Build an incident playbook before the incident
When a suspicious transfer occurs, the first minutes matter.
Do not design the response while money is already moving.
Decide in advance:
who contacts the bank;
who freezes credentials;
who preserves evidence;
who contacts the genuine vendor;
who suspends access;
and who reports the incident.
Satgas PASTI advises victims to retain phone numbers, conversations with timestamps, transfer evidence, account or entity details and relevant URLs, rather than deleting evidence before it is documented.[1]
Financial scam victims can also report to IASC to support account-blocking and fund-recovery efforts.[1]
Treat payment QR codes as operational assets
QRIS is now routine business infrastructure.
That means merchants should protect QR materials and administrative access.
Check that physical codes have not been replaced or covered.
Control who can change settlement settings.
Protect devices and administrator accounts used for dynamic payment generation.
Many fraud scenarios do not require sophisticated hacking.
Changing the destination can be enough.
Strong passwords do not solve social engineering
Multi-factor authentication matters.
Password security matters.
Patching matters.
But an employee can still be persuaded to approve a legitimate transaction for the wrong purpose.
That is why cybersecurity and fraud control are related but different.
Cybersecurity protects systems.
Fraud controls protect decisions and money movement.
Bank Indonesia’s current payment-system framework explicitly integrates governance, risk management, internal controls and cyber resilience.[5][6]
Training cannot be the only defence
Employees need awareness.
Never share OTPs.
Verify identities.
Report suspicious requests.
Avoid unknown links.
But people become tired.
Busy.
Distracted.
Or simply convinced by a good impersonation.
A strong process assumes that someone will eventually make a mistake.
The goal is to ensure that one mistake does not automatically become a financial loss.
Controls do not need to be expensive
Small businesses may not have dedicated fraud platforms.
They can still maintain:
a locked vendor-bank master;
independent callbacks;
dual approvals;
transaction notifications;
daily reconciliation;
separate user accounts;
transfer limits;
and a checklist for beneficiary changes.
Some of the most effective controls are process design rather than software.
Think in three defensive layers
Before payment
Access controls.
Vendor verification.
Protected master data.
Approval thresholds.
Employee awareness.
During payment
Maker–checker.
Anomaly review.
Independent confirmation.
Transaction limits.
After payment
Reconciliation.
Alerts.
Audit trails.
Incident response.
Reporting.
The purpose is defence in depth.
If one layer fails, another remains.
Faster payments require faster controls
Digital systems allow money to move extremely quickly.
That is valuable.
But control processes designed for slower, manual payments may no longer be adequate.
If a transaction can leave the company within a minute, the fraud response cannot take two days to identify who should be called.
The next operational challenge is not slowing payments down.
It is making verification move at digital speed.
Scam risk is not merely a technology problem
Hundreds of thousands of reports have reached IASC.
Hundreds of thousands of accounts have been blocked.
Hundreds of billions of rupiah have been stopped from moving further.[1]
That scale means businesses need to move beyond a generic warning:
“Be careful of scams.”
The more useful question is:
“If one employee believes a convincing fake instruction, what control still prevents company money from leaving?”
That is the real test.
A resilient company is not one that assumes its people will never be fooled.
It is one designed so that fooling one person is not enough to complete the fraud.
- [1] Financial Services Authority / Satgas PASTI. 25,000 Illegal Financial Activity Complaints and Rp724 Billion in Scam-Related Funds Blocked by IASC. August–September 2026.
- [2] Bank Indonesia. Indonesia Credit Card and 0% QRIS MDR Policy. August 17, 2026.
- [3] Bank Indonesia. BI-FAST fraud-management regulations and transaction-level detection requirements.
- [4] Bank Indonesia. Retail payment infrastructure / GPN functions including reconciliation, security, fraud prevention and risk management.
- [5] Bank Indonesia Regulation No. 10/2025 on Payment-System Industry Regulation.
- [6] Bank Indonesia Regulation No. 2/2024 on Information-System Security and Cyber Resilience.
- IASC data cover public reports broadly and are not a count of business fraud cases alone.
- Rp724.1 billion represents scam-related funds successfully blocked, not total national scam losses.
- Maker–checker, callback verification, payment thresholds and refund controls are practical risk-management frameworks rather than universal regulatory requirements for all businesses.
Published: September 15, 2026